Why Persistence Matters
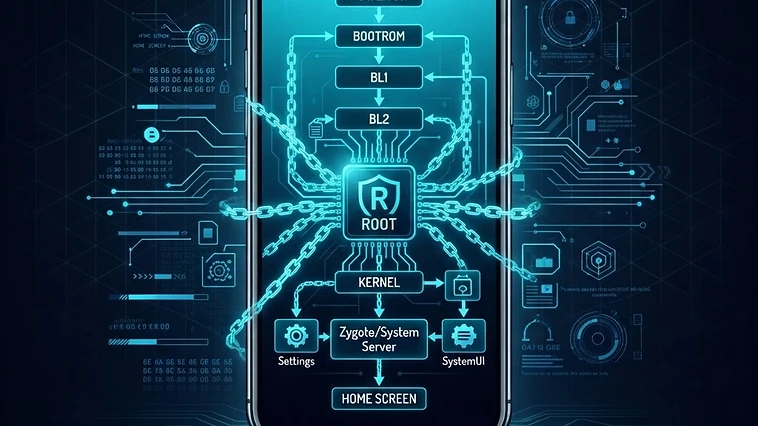
A spyware implant that gets killed on reboot is useless. Persistence is what keeps the implant running across reboots, app updates, and system cleanup attempts. Understanding how ZeroDayRAT persists on a device is essential for both detection and removal, because if you remove the implant but miss the persistence mechanism, the implant can come back.
This analysis from the ZeroDayRAT Intelligence Center covers the reported persistence mechanisms used by ZeroDayRAT on Android, how each one works, and how to break it. For the full technical breakdown, see our technical analysis. For the removal process, see our removal guide.
Mechanism 1: Accessibility Service Auto-Start
How It Works
The accessibility service is the single most important persistence mechanism for Android spyware, and ZeroDayRAT uses it. When an app is granted accessibility access, the system binds to it and starts it automatically on boot. The app runs as a persistent background service that the system is reluctant to kill, because killing an accessibility service would break accessibility for users who depend on it.
This means that once ZeroDayRAT gets accessibility access, it survives reboots without any additional effort. The system itself ensures the implant starts back up after every restart. This is why the accessibility service is so heavily abused by spyware, it is both a capability enabler (keylogging, overlay attacks, interaction hijacking) and a persistence mechanism.
Evidence Classification
Accessibility service abuse is Confirmed as a general Android spyware technique and Reported as a ZeroDayRAT persistence mechanism. Multiple researchers have documented the pattern. For the full analysis of how the accessibility service is abused, see our Android accessibility spyware vector analysis.
How to Break It
To break this persistence, revoke accessibility access. Go to Settings > Accessibility, find the suspicious app, and toggle off accessibility access. Once revoked, the app no longer auto-starts on boot and loses its keylogging and overlay capabilities. This is the single most important step in removing Android spyware.
Mechanism 2: Device Admin Privileges
How It Works
Device admin is an Android feature designed for enterprise management that gives an app elevated privileges. A device admin app can enforce security policies, wipe the device, and, critically for spyware, prevent uninstallation. When an app has device admin privileges, the uninstall button in Settings > Apps is grayed out, and the user cannot remove the app through normal means.
ZeroDayRAT is Reported to request device admin privileges as part of its installation flow. The request is typically framed with a plausible justification, like "this app needs device admin to protect your data," and the user grants it without understanding the implications. Once granted, the spyware is much harder to remove.
Evidence Classification
Device admin abuse is Confirmed as a general Android malware technique and Reported as a ZeroDayRAT feature. The technique is used by many Android malware families to resist uninstallation.
How to Break It
To break this persistence, revoke device admin access first, then uninstall. Go to Settings > Security > Device admin apps, find the suspicious app, and deactivate it. Once deactivated, the uninstall button in Settings > Apps becomes available, and you can remove the app normally. Never skip this step, or the uninstall will fail.
Mechanism 3: Foreground Services
How It Works
Android can kill background apps to free memory, which is a problem for spyware that needs to keep running. Foreground services are the solution. A foreground service is a service that shows a persistent notification and is therefore considered important enough that the system will not kill it. The user sees a notification, but spyware can make the notification inconspicuous, disguised as a system process or hidden behind a generic label.
ZeroDayRAT is Reported to use foreground services to keep the implant alive. The persistent notification is required by Android for foreground services, but the spyware makes it as unnoticeable as possible. On some Android versions, the notification can be minimized or hidden in a way that the user is unlikely to see it.
Evidence Classification
Foreground service abuse is Confirmed as a general Android technique and Reported as a ZeroDayRAT feature. The technique is common across Android spyware and banking trojans.
How to Break It
To break this persistence, force stop the app. Go to Settings > Apps, find the suspicious app, and force stop it. This kills the foreground service. Then revoke permissions and uninstall as described above. If the app restarts itself after force stop, it has another persistence mechanism active, likely accessibility or device admin, and you need to break those first.
Mechanism 4: Icon Hiding
How It Works
After installation, ZeroDayRAT is Reported to hide its app icon from the launcher. The app still exists in the system, and it still runs, but it does not appear in the app drawer. This makes it harder for the victim to notice the app is installed, and harder to find when they go looking for it.
The technique uses a feature of Android's package manager that allows an app to disable its own launcher component. The app sets its launcher activity to disabled, which removes it from the app drawer, while keeping the rest of the app active. The app can still be found in Settings > Apps, but most users do not look there.
Evidence Classification
Icon hiding is Confirmed as a general Android spyware technique and Reported as a ZeroDayRAT feature. The technique is used by many commercial RATs to avoid detection.
How to Break It
To find a hidden app, go to Settings > Apps and look through the full app list. The app drawer only shows apps with a launcher icon, but Settings > Apps shows everything. Look for apps you do not recognize, apps with generic names, or apps with no icon. Once you find the suspicious app, follow the removal steps above.
Mechanism 5: Boot Completed Receiver
How It Works
Android apps can register a broadcast receiver for the BOOT_COMPLETED intent, which fires when the device finishes booting. An app with this receiver can start itself automatically after every reboot. This is a standard Android feature used by legitimate apps like messaging and email clients, but it is also abused by spyware.
ZeroDayRAT is Reported to use a boot completed receiver as a backup persistence mechanism. Even if the foreground service is killed, the boot receiver ensures the implant restarts on the next reboot. Combined with accessibility auto-start, this gives the spyware multiple layers of persistence.
Evidence Classification
Boot completed receiver abuse is Confirmed as a general Android technique and Reported as a ZeroDayRAT feature. The technique is standard across Android malware.
How to Break It
You cannot directly disable a boot completed receiver through settings, but uninstalling the app removes all of its receivers. The key is to ensure you actually uninstall the app, not just force stop it. If you force stop the app but leave it installed, the boot receiver will restart it on the next reboot. Always complete the full removal process.
Mechanism 6: Work Profile Abuse (Reported)
How It Works
Android work profiles are designed for enterprise use, creating an isolated space on the device for work apps. Some spyware is Reported to create a work profile to gain persistence and isolation. Apps in a work profile can run independently of the main profile and are harder to detect through normal settings inspection.
This is a more advanced technique and has not been confirmed in ZeroDayRAT specifically. We classify it as Reported and Unconfirmed. For more on this technique, see our Android security guide.
How to Break It
To check for a work profile, go to Settings and look for a Work profile section. If you see one you did not create, remove it. Removing the work profile deletes all apps in it, including any spyware.
iOS Persistence (Limited)
iOS persistence is fundamentally different because of the platform's restrictions. There is no accessibility service equivalent, no device admin, and no boot completed receiver. The main persistence mechanisms on iOS are MDM enrollment and configuration profiles, both of which require social engineering to install.
If ZeroDayRAT is installed on iOS via MDM or a configuration profile, the persistence comes from the management framework, not from the app itself. Removing the profile removes the persistence. For the full iOS analysis, see our iOS security guide.
Breaking Persistence: The Full Process
Step 1: Revoke Accessibility
Go to Settings > Accessibility and revoke access for the suspicious app. This breaks the most important persistence mechanism.
Step 2: Revoke Device Admin
Go to Settings > Security > Device admin apps and deactivate the suspicious app. This makes the app uninstallable.
Step 3: Force Stop
Go to Settings > Apps, find the suspicious app, and force stop it. This kills the foreground service and any running processes.
Step 4: Revoke All Permissions
In the app's permission settings, revoke every permission. This stops data collection even if the uninstall fails.
Step 5: Uninstall
In Settings > Apps, uninstall the app. With accessibility and device admin revoked, the uninstall button should be available.
Step 6: Check for Work Profile
Go to Settings and check for a Work profile section. If one exists that you did not create, remove it.
Step 7: Remove Configuration Profiles
Check Settings > Security or Settings > Network for any configuration profiles you did not install and remove them.
For the full removal process with evidence preservation steps, see our removal guide and incident response playbook.
Frequently Asked Questions
How does ZeroDayRAT survive a reboot?
ZeroDayRAT survives reboots primarily through the accessibility service, which the system auto-starts on boot. It may also use a boot completed receiver as a backup. Once accessibility is revoked, the main persistence mechanism is broken.
Why can I not uninstall ZeroDayRAT?
If the uninstall button is grayed out, the app likely has device admin privileges. Go to Settings > Security > Device admin apps, deactivate the suspicious app, then return to Settings > Apps and uninstall it.
How does ZeroDayRAT hide its icon?
ZeroDayRAT is reported to disable its launcher component after installation, which removes it from the app drawer. The app still exists and runs, but is not visible in the app drawer. You can find it in Settings > Apps, which shows all installed apps regardless of launcher icon.
Does ZeroDayRAT persist on iOS?
iOS persistence is limited and relies on MDM enrollment or configuration profiles rather than app-level mechanisms. If ZeroDayRAT is installed on iOS via a profile, removing the profile removes the persistence. There is no accessibility service or device admin equivalent on iOS.
How do I permanently remove ZeroDayRAT persistence?
Revoke accessibility access, revoke device admin, force stop the app, revoke all permissions, uninstall the app, check for and remove any work profile, and remove any configuration profiles you did not install. If you cannot fully break persistence, factory reset the device and restore only personal data, not apps.