Intelligence Blog
Mobile Spyware & Offensive Cyber Analysis
30 in-depth articles covering mobile spyware, malware, banking trojans, RATs, and the offensive cyber threat landscape — with detection guidance, incident response playbooks, and threat analysis.


The Evolution of Mobile Spyware: From FlexiSPY to ZeroDayRAT
A comprehensive history of mobile surveillance tools — from early consumer stalkerware to commercial malware-as-a-service platforms like ZeroDayRAT. Learn how the threat landscape has transformed over two decades.

How Android Accessibility Services Became the Ultimate Spyware Vector
Android's Accessibility Service was designed to help disabled users. Instead, it has become the most powerful spyware vector on mobile. Learn how it works and how to defend against it.

Zero-Click Exploits Explained: The Holy Grail of Mobile Hacking
Zero-click exploits require no user interaction. They are the most sophisticated and expensive attacks in mobile hacking. Learn how they work, who uses them, and how to defend against them.

The Commercial Spyware Economy: Who's Buying and Who's Selling
A deep dive into the global marketplace for mobile surveillance tools — from mercenary spyware companies to dark web malware-as-a-service operations. Understand the economics driving the spyware industry.

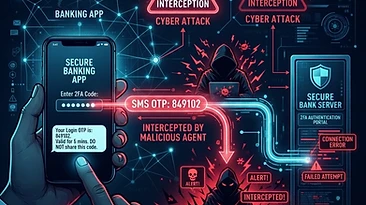
SMS OTP Interception: How Banking Trojans Defeat 2FA
SMS-based two-factor authentication is used by billions of people, but mobile spyware can intercept OTP codes before they ever reach the user. Learn how this attack works and what to do about it.


The Pegasus Playbook: Inside NSO Group's Surveillance Empire
Pegasus by NSO Group is the most documented mercenary spyware in history. Learn about its capabilities, its victims, and the legal battles that followed its exposure.

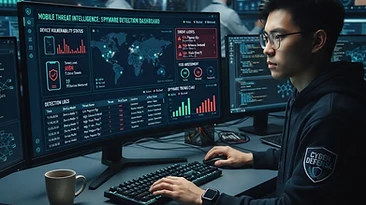
Detecting Mobile Spyware: A Defender's Complete Guide
A comprehensive guide to detecting mobile spyware on Android and iOS devices — from permission auditing to forensic analysis. Learn the tools, techniques, and strategies for identifying compromise.

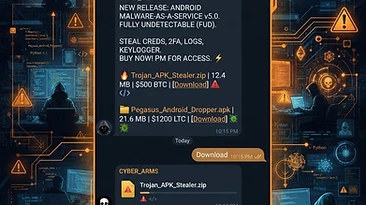
The Rise of Malware-as-a-Service on Telegram
Telegram has become the primary distribution channel for commercial mobile malware. Learn how MaaS operators use Telegram channels, bots, and cryptocurrency to sell spyware globally.

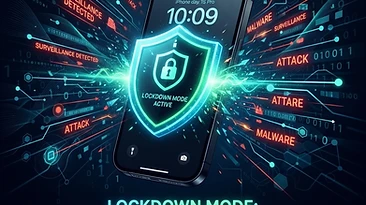
iOS Lockdown Mode: Does It Actually Protect Against Spyware?
Apple's Lockdown Mode is the most aggressive mobile security feature ever shipped. But does it actually work? Learn what it protects against, what it doesn't, and who should enable it.

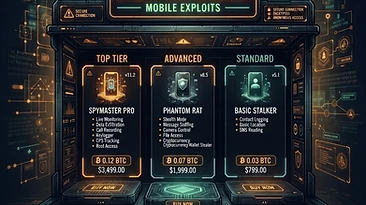
The Dark Web Market for Mobile RATs: A Price Analysis
How much does mobile spyware cost on the dark web? A detailed price analysis of mobile RATs, banking trojans, and surveillance tools available on underground marketplaces.

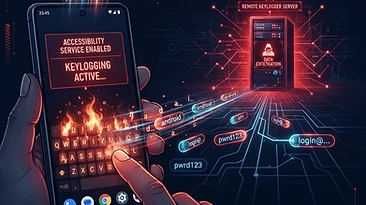
Keyloggers on Android: How Accessibility Abuse Captures Everything
Android keyloggers don't need custom keyboards — they use accessibility services to capture every keystroke. Learn how this attack works and how to detect it.


MDM Profiles as a Spyware Vector on iOS
iOS is more locked down than Android, but MDM configuration profiles can bypass many restrictions. Learn how MDM profiles are abused for surveillance and how to detect them.


The Supply Chain Attack Chain: From Developer to Victim's Phone
Supply chain attacks compromise the software development process itself. Learn how mobile apps can be infected before they ever reach the app store, and how this affects end users.

How Mobile Spyware Evades Google Play Protect
Google Play Protect scans billions of apps, but spyware developers have evolved sophisticated evasion techniques. Learn how mobile malware bypasses the world's largest mobile security scanner.

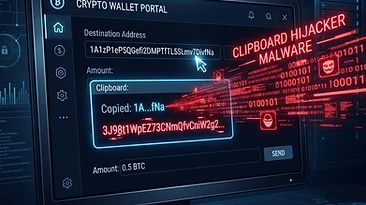
Clipboard Hijacking: The Silent Cryptocurrency Thief
Clipboard hijacking malware silently replaces cryptocurrency wallet addresses when you copy them. Learn how this attack works and how to protect your crypto.

The Forensics of Mobile Spyware: Using MVT to Detect Compromise
MVT (Mobile Verification Toolkit) is the gold standard for mobile spyware forensics. Learn how to use it, what it can detect, and its limitations in identifying advanced spyware.

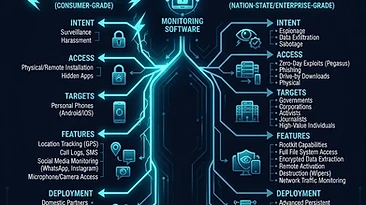
Stalkerware vs Spyware: Understanding the Threat Taxonomy
Stalkerware, commercial spyware, and mercenary spyware are all forms of mobile surveillance, but they differ in purpose, cost, and targeting. Learn the taxonomy and why it matters for defense.

How Nation-States Use Commercial Spyware for Surveillance
Governments are increasingly using commercially available spyware instead of developing their own. Learn why commercial spyware is attractive to nation-states and what it means for global surveillance.

The Zero-Day Market: Who Sells Mobile Exploits and for How Much
The zero-day exploit market is a multi-million dollar industry. Learn who buys and sells mobile exploits, how much they cost, and why this market is critical to understanding the spyware ecosystem.

Camera and Microphone Surveillance: How RATs Turn Phones into Bugs
Mobile RATs can silently activate your camera and microphone, turning your phone into a remote surveillance device. Learn how this works and how to detect it.


Enterprise Mobile Security: Protecting Executives from Targeted Spyware
Executives are prime targets for mobile spyware. Learn how enterprises can protect their leadership from targeted surveillance, from MDM policies to executive protection programs.


The Psychology of Social Engineering in Mobile Spyware Delivery
Mobile spyware doesn't exploit software vulnerabilities — it exploits human psychology. Learn the social engineering techniques used to trick users into installing spyware.

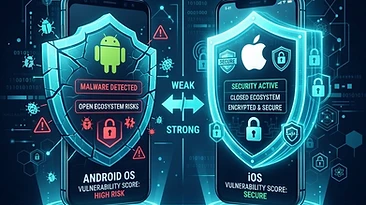
Android vs iOS Security: Which Platform Is Safer from Spyware?
The debate between Android and iOS security is complex. Learn the real differences in spyware resistance, platform-specific vulnerabilities, and which platform is safer for different users.

The Role of Telegram in the Commercial Spyware Ecosystem
Telegram has become the backbone of the commercial spyware industry. Learn how spyware is sold, supported, and distributed through Telegram channels and bots.

How to Build a Mobile Threat Intelligence Program
A practical guide to building a mobile threat intelligence program — from threat modeling to IOC collection, analysis, and dissemination. Learn how to stay ahead of mobile spyware threats.

The Legal and Ethical Landscape of Commercial Spyware
The commercial spyware industry operates in a complex legal and ethical landscape. Learn about the laws, regulations, and ethical frameworks that govern (or fail to govern) the spyware industry.

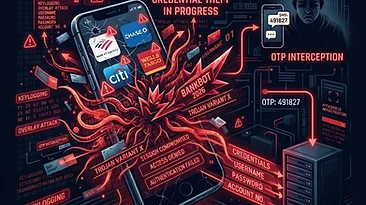
Banking Trojans of 2026: Anatsa, FluBot, and Beyond
Banking trojans are among the most financially damaging mobile threats. Learn about the major banking trojan families of 2026, their capabilities, and how to defend against them.

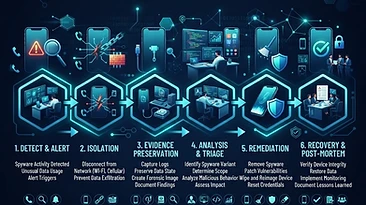
Incident Response for Mobile Spyware: A Step-by-Step Playbook
A complete incident response playbook for suspected mobile spyware compromise. Learn what to do from detection through remediation, with specific steps for Android and iOS.

The Future of Mobile Spyware: AI-Powered Surveillance and Beyond
What does the future hold for mobile spyware? From AI-powered surveillance to new attack surfaces, learn about the emerging threats that will shape the next decade of mobile security.