Why Platform Matters for ZeroDayRAT
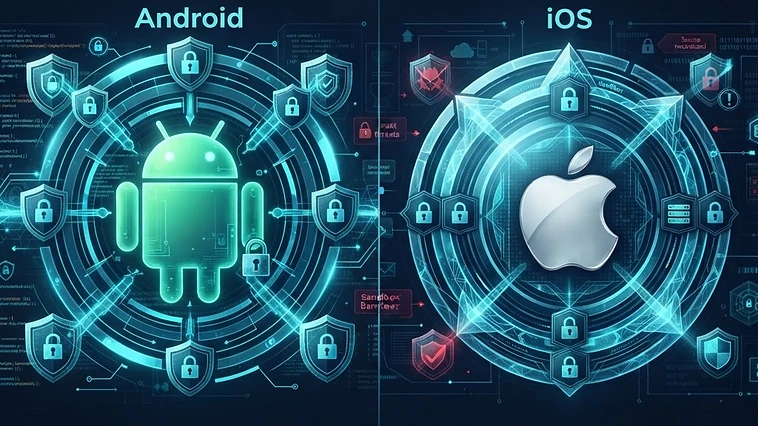
ZeroDayRAT is advertised as a cross-platform mobile spyware product, targeting both Android and iOS. But the technical reality of each platform means the threat profile is not symmetric. Android and iOS have fundamentally different security architectures, permission models, and distribution constraints, and these differences determine what spyware can realistically do on each. This analysis from the ZeroDayRAT Intelligence Center compares the two platforms and explains why most advertised iOS capabilities remain unconfirmed.
For platform-specific defensive guidance, see our Android security guide and iOS security guide.
Android: The Primary Target
Why Android Is More Vulnerable
Android is the primary target for ZeroDayRAT and most commercial mobile spyware. The reasons are structural. Android allows installation from unknown sources, which means a user can install an APK from anywhere, not just the Play Store. Android's permission model, while improved in recent versions, still allows broad permission grants that enable surveillance. And the accessibility service, designed for users with disabilities, is routinely abused by spyware for keylogging, overlay attacks, and interaction hijacking.
The Android version of ZeroDayRAT is the most documented. Multiple researchers including iVerify, ThaiCERT, and Cyberthint have analyzed Android payloads, and the core capabilities, location tracking, SMS interception, notification access, and keylogging via accessibility, are Confirmed or Reported. For the full capability breakdown, see our capabilities page.
Documented Android Capabilities
The following Android capabilities have been Reported or Confirmed by independent researchers. Location tracking via GPS and network positioning is Confirmed. SMS interception using the SMS permission is Confirmed. Notification access for intercepting OTP codes and messaging app notifications is Confirmed. Keylogging and overlay attacks via the accessibility service are Reported. Screen capture via MediaProjection is Reported. Camera and microphone access is Advertised with partial Reported confirmation.
The permission combination that enables all of this is distinctive. An app requesting accessibility plus SMS plus notifications plus location plus camera plus microphone is spyware until proven otherwise. No legitimate app needs this combination. For the full permission-to-capability mapping, see our capability-to-permission map.
Android Delivery
Android delivery is primarily through sideloaded APKs. The victim receives a phishing message with a link to an APK, downloads it, and installs it after bypassing the unknown-source warning. Modern Android shows a warning, but social engineering gets users past it. For the full delivery analysis, see our delivery vectors blog post.
Android Persistence
Android spyware persists through a combination of techniques. The accessibility service itself provides persistence because it auto-starts on boot. Device admin privileges, if granted, make the app harder to uninstall. The app may hide its icon after installation, making it invisible in the app drawer. And the app may use foreground services to avoid being killed by the system. For more on persistence, see our attack chain analysis.
iOS: The Harder Target
Why iOS Is Harder to Compromise
iOS is a harder target for commercial spyware for structural reasons. Apple's code signing means apps must be signed by Apple or an enterprise certificate, and the App Store review process catches a lot of malware before it reaches users. iOS sandboxing is strict, limiting what an app can access even after installation. And the permission model is more restrictive, with each sensitive capability requiring explicit user consent that must be renewed periodically.
These constraints do not make iOS immune, but they make silent surveillance much harder. The iOS version of ZeroDayRAT is advertised with the same capabilities as Android, but most of these claims are Unconfirmed because the technical constraints make them implausible without a jailbreak or MDM enrollment. For a deeper look at iOS security architecture, see our iOS security guide.
Reported iOS Delivery Methods
The delivery methods Reported for iOS ZeroDayRAT include MDM profile abuse and enterprise certificate abuse. MDM profile abuse involves tricking the user into installing a malicious configuration profile, which gives the attacker management control over the device. Enterprise certificate abuse involves using a stolen or misused enterprise certificate to sign the malicious app, bypassing the App Store.
Both methods require social engineering to get the user to install the profile or trust the certificate. Neither has been independently confirmed in ZeroDayRAT specifically. We classify iOS delivery as Reported and Unconfirmed. For more on MDM as an attack vector, see our MDM profiles analysis.
iOS Capability Constraints
Even if an iOS implant is installed, the sandbox limits what it can do. Silent camera and microphone access is extremely difficult because iOS requires apps to be in the foreground and show an indicator when the camera or microphone is active. Background location access is restricted and shows an indicator. SMS interception is not possible through a standard API. Notification access is limited. Keylogging is not possible without a custom keyboard, which the user must explicitly enable.
This is why most advertised iOS capabilities for ZeroDayRAT are classified as Advertised and Unconfirmed. The seller claims the features work, but the technical constraints of iOS make many of those claims implausible without a jailbreak, and there is no public evidence that ZeroDayRAT jailbreaks devices. For the full comparison, see our Android vs iOS security analysis.
Lockdown Mode
For high-risk iOS users, Lockdown Mode is the single most effective defensive measure. It restricts features that are commonly abused by sophisticated attacks, including blocking most message attachments, disabling link previews, blocking wired connections when the device is locked, and blocking configuration profile installation. While Lockdown Mode is designed for mercenary spyware like Pegasus, it also reduces the attack surface for commercial spyware. See our Lockdown Mode analysis for details.
Comparative Threat Summary
Attack Surface
Android has a larger attack surface for commercial spyware because of sideloading, the accessibility service, and a more permissive permission model. iOS has a smaller attack surface because of code signing, sandboxing, and a more restrictive permission model. This is not a value judgment about which platform is better, it is a factual statement about where commercial spyware invests its effort.
Capability Realism
On Android, the advertised capabilities of ZeroDayRAT are largely plausible and many are confirmed. On iOS, the advertised capabilities are largely implausible without a jailbreak or MDM enrollment, and most remain unconfirmed. A user on iOS is at lower risk from ZeroDayRAT specifically, though not from all mobile spyware.
Detection Difficulty
Android infections are easier to detect because the permission combinations are distinctive and the artifacts are visible in settings. iOS infections are harder to detect because the platform restricts what inspection tools can do, but tools like MVT can analyze backup and analytics data for indicators. For the full detection guide, see our detection page.
Recovery
Recovering from an Android infection involves uninstalling the malicious app, revoking permissions, and in severe cases, factory resetting. Recovering from an iOS infection involves removing configuration profiles, unenrolling from MDM, and in severe cases, factory resetting. For the full recovery process, see our incident response playbook.
Defensive Recommendations by Platform
Android Defenses
Do not install apps from outside the Play Store unless you absolutely trust the source. Audit accessibility settings for unknown apps. Audit installed apps for dangerous permission combinations. Use Google Play Protect. For organizations, use Android Enterprise MDM to restrict sideloading and dangerous permissions. For high-risk users, consider Android's advanced protection program.
iOS Defenses
Do not install configuration profiles from untrusted sources. Check Settings > General > VPN and Device Management for unexpected profiles. Do not trust enterprise certificates from unknown organizations. Enable Lockdown Mode if you are a high-risk user. Keep iOS updated. For organizations, use Apple Business Manager and MDM to manage devices.
Frequently Asked Questions
Is ZeroDayRAT worse on Android or iOS?
ZeroDayRAT is more capable on Android because of sideloading, the accessibility service, and a more permissive permission model. On iOS, most advertised capabilities are unconfirmed because the platform's sandboxing and permission controls make silent surveillance very difficult without a jailbreak.
Can ZeroDayRAT infect iPhone?
An iOS version is advertised, but most iOS capability claims are unconfirmed. Reported iOS delivery methods include MDM profile abuse and enterprise certificate abuse, both of which require social engineering. There is no confirmed zero-click iOS delivery path.
Does ZeroDayRAT jailbreak iOS?
There is no public evidence that ZeroDayRAT jailbreaks iOS devices. Without a jailbreak, most advertised iOS surveillance capabilities are implausible because of iOS sandboxing and permission controls. The iOS version appears to rely on social engineering rather than exploitation.
Is iOS safer than Android from ZeroDayRAT?
For ZeroDayRAT specifically, iOS is lower risk because the platform's constraints make most advertised capabilities implausible. However, no platform is immune to all mobile spyware, and iOS users should still follow platform-specific security guidance including avoiding configuration profiles from untrusted sources.
Should I use Lockdown Mode to protect against ZeroDayRAT?
Lockdown Mode is designed for mercenary spyware like Pegasus, but it also reduces the attack surface for commercial spyware including ZeroDayRAT. High-risk users may benefit from enabling it. For most users, following standard iOS security guidance is sufficient.